The Ultimate Guide to MiCA Compliance 2026

MiCA compliance in 2026 means crypto businesses, wallet teams, stablecoin issuers, and users need to understand how the EU's Markets in Crypto-Assets Regulation changes the rules for custody, issuance, trading, disclosures, and self-custody. The rules apply differently depending on the crypto-asset, the service being provided, the legal entity providing it, and whether that entity controls customer assets or private keys.
Why MiCA compliance matters in 2026
MiCA is the EU's harmonized crypto regulatory framework, formally known as Regulation (EU) 2023/1114. It creates a common rulebook for crypto-asset issuers, stablecoin issuers, and crypto-asset service providers, often called CASPs. The official legal text is available through EUR-Lex, while ESMA maintains a dedicated supervisory resource for the regulation on its Markets in Crypto-Assets Regulation page.
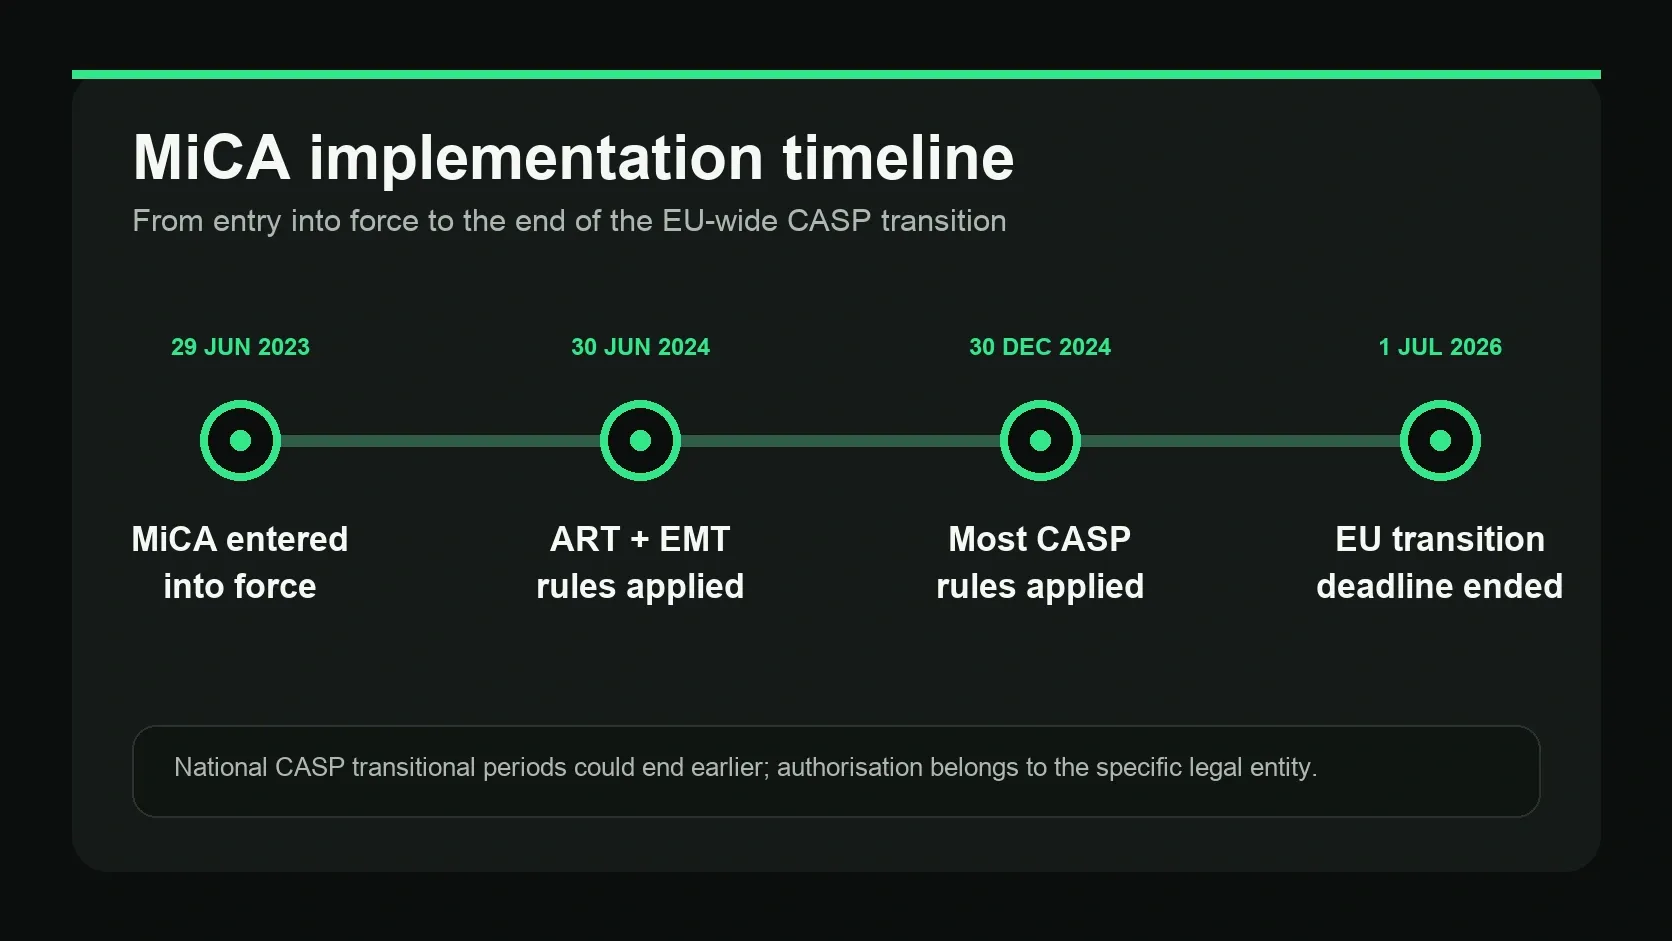
The key reason 2026 matters is timing. MiCA entered into force on June 29, 2023. Rules for asset-referenced tokens and e-money tokens began applying on June 30, 2024, and most CASP rules began applying on December 30, 2024. Article 143 allowed eligible providers to continue under national transitional arrangements until they received or were refused MiCA authorisation, or until the applicable national transition ended. ESMA confirmed that the final EU-wide transition deadline expired on July 1, 2026. Providers relying on that transition can no longer treat a pre-MiCA national registration as a substitute for MiCA authorisation.
For users, MiCA compliance does not simply mean more paperwork for companies. It may affect which platforms operate in Europe, how stablecoins are listed, what disclosures token issuers provide, and how custodial services protect client assets. For wallet users, the most important distinction is whether a provider controls private keys or whether users retain self-custody.
MiCA compliance timeline and core definitions
MiCA uses specific legal categories. Understanding them helps users and builders avoid overgeneralized claims such as "all wallets are regulated" or "all DeFi is exempt." The European Commission explains that the regulation is designed to bring legal certainty to crypto-assets not already covered by existing EU financial services law through its crypto-assets policy page.
| Term | Practical meaning |
|---|---|
| Crypto-asset | A digital representation of value or rights that can be transferred and stored using distributed ledger technology or similar technology. |
| CASP | A crypto-asset service provider offering covered crypto services professionally to clients. |
| ART | An asset-referenced token designed to maintain stable value by referencing assets, rights, currencies, or a basket. |
| EMT | An e-money token designed to maintain stable value by referencing one official currency. |
| Custody and administration | Safekeeping or controlling crypto-assets or access keys on behalf of clients. |
| Crypto-asset white paper | A required disclosure document for certain token offers or admissions to trading. |
MiCA compliance also interacts with rules outside MiCA. For example, the EU Transfer of Funds Regulation, Regulation (EU) 2023/1113, extends Travel Rule-style information requirements to certain crypto-asset transfers involving regulated service providers. This is separate from MiCA, but it can affect CASPs and transfer-related processes. The legal text is available through EUR-Lex on the Transfer of Funds Regulation, and the EBA provides additional guidance through its Travel Rule guidelines.
Who needs MiCA compliance and what obligations apply
MiCA compliance mainly concerns parties that issue crypto-assets, offer stablecoins, or provide regulated crypto-asset services in or to the EU. These obligations are activity-based, so the same company may need different analyses for different products.
| Actor | Typical MiCA relevance |
|---|---|
| Token issuers | May need a white paper and fair, clear, not misleading disclosures. |
| ART issuers | May face authorization, reserve, redemption, governance, and disclosure rules. |
| EMT issuers | May face e-money-style obligations plus MiCA-specific requirements. |
| CASPs | May need authorization, governance, prudential safeguards, complaint handling, and operational controls. |
| Custodial wallet providers | May fall under custody rules if they safeguard or control user assets or private keys. |
| Trading platforms and exchanges | May need authorization and market integrity controls. |
| Non-custodial wallet software providers | Often analyzed differently from custodial providers, but facts and added services matter. |
CASP obligations can include authorization by a national competent authority, sound governance, own funds requirements, complaint handling, conflict-of-interest policies, safeguarding procedures where relevant, outsourcing controls, market abuse monitoring, and recordkeeping. ESMA's MiCA resources explain the regulator's role in technical standards, supervision, and implementation.
Stablecoins require special attention. The EBA explains that issuers of ARTs and EMTs need the relevant authorisation to carry out covered activities in the EU, with additional requirements for significant tokens. In practice, users may see platforms review stablecoin availability, disclosures, and regional access as supervision develops.
A practical takeaway is simple: businesses should map their exact services before making claims. Issuing a token, operating a trading platform, executing orders, providing exchange services, controlling keys, or offering portfolio advice can create different obligations. Pure software, infrastructure, and user-controlled wallets may require a different analysis, but that does not remove the need for careful legal review.
How to verify a provider's MiCA authorisation
MiCA authorisation belongs to a specific legal entity, not automatically to every company using the same brand. A provider's old national VASP registration, an application announcement, or a licence held by another group company is not enough on its own.
Before relying on a provider's MiCA status:
- Identify the legal entity named in the terms or client agreement.
- Check the ESMA Interim MiCA Register and the relevant national competent authority's register.
- Match the legal name and, where available, the legal entity identifier to the entity serving the account.
- Review which crypto-asset services the authorisation covers.
- Confirm whether cross-border services are provided through the authorised EU entity rather than a different group company.
ESMA also maintains information on entities reported as providing crypto-asset services without the necessary authorisation. A register check is more reliable than a generic claim that a brand is "MiCA compliant."
MiCA compliance for wallets, DeFi, DApps, and cross-chain swaps
MiCA draws a critical distinction between custodial and non-custodial models. A custodial wallet provider may control or safeguard assets or private keys on behalf of users. A non-custodial wallet lets users control private keys and sign transactions themselves.
FoxWallet is built around the non-custodial model. Users retain control of their private keys and assets, and FoxWallet does not hold user funds. For readers comparing wallet models, FoxWallet's guide to a secure multi-chain non-custodial wallet explains how local encrypted storage, multi-chain visibility, in-wallet swaps, and risk alerts fit together.
Non-custodial does not mean "no risk." Users remain responsible for seed phrase backup, transaction review, DApp approvals, phishing avoidance, and smart contract risk. For practical onboarding, FoxWallet's guide on how to set up a secure crypto wallet covers official downloads, backup hygiene, local encryption, and safe Web3 access.
DeFi and DApps require careful language. ESMA and EBA have noted that fully decentralized arrangements may be treated differently, but interfaces, operators, governance structures, or identifiable service providers can create case-by-case questions. The ESMA Article 142 report on crypto-asset market developments is available as an official supervisory report.
Cross-chain swaps also require fact-specific analysis. A user-initiated non-custodial route is different from a centralized intermediary that controls assets, executes orders, or provides regulated exchange or transfer services. On FoxWallet mobile, same-chain Swap is provided through 1inch on supported networks and Bridge routes are provided through LI.FI on supported networks. For a deeper technical explanation, see FoxWallet's guide to how cross-chain swaps work.
Staking is separate from cross-chain swaps. It can involve different structures, such as direct staking, delegation, pooled services, liquid staking, or custodial arrangements. Users and service providers should avoid treating staking and cross-chain swapping as the same legal or operational category.
How FoxWallet supports safer self-custody in a MiCA compliance era
FoxWallet does not claim that using a wallet makes a person or business MiCA compliant. MiCA compliance depends on facts, jurisdiction, custody and control, service design, and how crypto services are offered in or to the EU. What FoxWallet does provide is a security-first, non-custodial environment for users who want to manage assets across chains while maintaining control of their private keys.
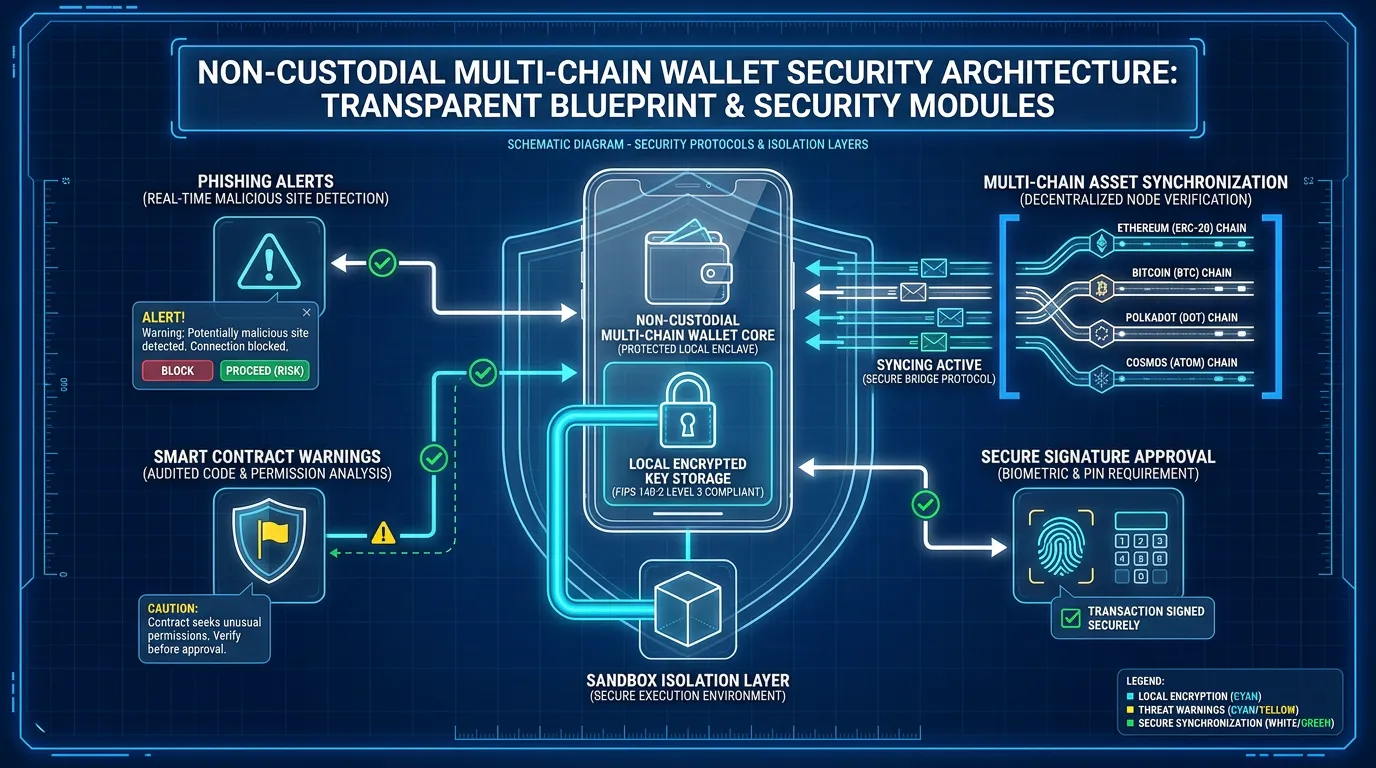
FoxWallet's mobile app supports multi-chain asset management, DApp access, same-chain swaps, and cross-chain bridge routes on supported networks. The browser extension is a narrower product surface for basic wallet actions on EVM networks and Aleo; it should not be assumed to have feature parity with the mobile app.
Key FoxWallet capabilities include:
| Capability | User benefit |
|---|---|
| Non-custodial architecture | Users control private keys and assets. |
| Local key storage | Private keys and recovery material are stored locally in encrypted form. |
| Multi-chain asset management | Users can view and manage assets across supported networks. |
| Built-in DApp access | Mobile users can connect to supported DApps from the wallet. |
| Mobile Swap | 1inch provides same-chain swap routing on supported networks. |
| Mobile Bridge | LI.FI provides cross-chain bridge routes on supported networks. |
| Security controls | The mobile app includes Connected Sites management, phishing-site blocking, high-risk signature warnings, and malicious-authorization checks. |
For stablecoin users, regional rules and platform support may change as MiCA compliance expectations mature. FoxWallet's guide to a multi-chain stablecoin wallet explains chain-specific stablecoin management, fee visibility, and self-custody considerations. For swap risk, the decentralized swap safety checklist covers approvals, slippage, bridge assumptions, and transaction review. Users who want to evaluate safety features can also review FoxWallet's article on wallet security features in 2026.
MiCA may improve standards for regulated entities, but it does not eliminate smart contract bugs, private key loss, phishing, malicious DApps, bridge risk, liquidity fragmentation, token volatility, or user signing mistakes. A security-first wallet helps reduce operational friction and improve user awareness, but users must still verify transactions and understand the risks of self-custody.
MiCA compliance checklist for 2026
A concise checklist helps separate legal obligations from user safety practices.
| Checklist area | Action |
|---|---|
| Scope | Identify whether the activity involves issuance, custody, exchange, transfer, trading platform operation, advice, or portfolio management. |
| Custody model | Confirm whether a provider controls assets or private keys. |
| Stablecoins | Classify assets as ARTs, EMTs, or another category where relevant. |
| CASP status | Determine whether authorization or notification is required. |
| Disclosures | Review white papers, marketing communications, fees, and risk statements. |
| Consumer protection | Maintain complaint handling, clear communications, and conflict controls where applicable. |
| Operational risk | Review cybersecurity, outsourcing, recordkeeping, and continuity controls. |
| Self-custody safety | Back up seed phrases, verify DApps, review approvals, and use transaction risk alerts. |
MiCA compliance FAQ
What is MiCA compliance?
MiCA compliance means meeting the obligations that apply under Regulation (EU) 2023/1114 to a particular crypto-asset, issuer, offeror, or crypto-asset service. The requirements depend on the activity and can include authorisation, disclosures, governance, prudential safeguards, custody controls, complaints handling, and market-abuse procedures.
Does a crypto company need MiCA authorisation in 2026?
An entity providing a crypto-asset service covered by MiCA to EU clients generally needs the appropriate MiCA authorisation unless a specific exemption applies. The EU-wide CASP transitional period ended on July 1, 2026, although some national transitions ended earlier.
Is a VASP registration the same as MiCA authorisation?
No. A pre-MiCA national VASP registration and a MiCA CASP authorisation are different statuses. Check the specific legal entity in the ESMA and national competent-authority registers.
Does MiCA regulate non-custodial wallets?
MiCA does not treat every piece of self-custody wallet software as a custodial CASP. The analysis depends on the services provided, who controls the assets or private keys, and whether regulated crypto-asset services are offered professionally. Third-party services accessed through a wallet may have their own regulatory status.
Does MiCA make crypto safe?
No. MiCA introduces requirements for covered issuers and service providers, but it does not eliminate market volatility, smart-contract bugs, phishing, private-key loss, bridge risk, or transaction mistakes.
The safest conclusion is measured: MiCA compliance is a regulatory obligation for covered businesses, not a simple badge for every crypto product. For users, the regulation makes custody models, stablecoin rules, provider authorisation, and risk disclosures more important. For self-custody, FoxWallet offers a multi-chain, non-custodial wallet experience where users control their private keys while managing supported assets, DApps, swaps, bridge routes, and other on-chain activity.
This article is for informational and educational purposes only and does not constitute legal, regulatory, financial, tax, or investment advice. MiCA applicability depends on facts, service structure, jurisdiction, custody and control model, and how services are offered in or to the EU. Businesses should consult qualified legal counsel before making compliance decisions.